



AI · Article
Fake Security Tools on GitHub Infect More Than 2,000 Windows PCs
데일리시큐 ·
At a glance
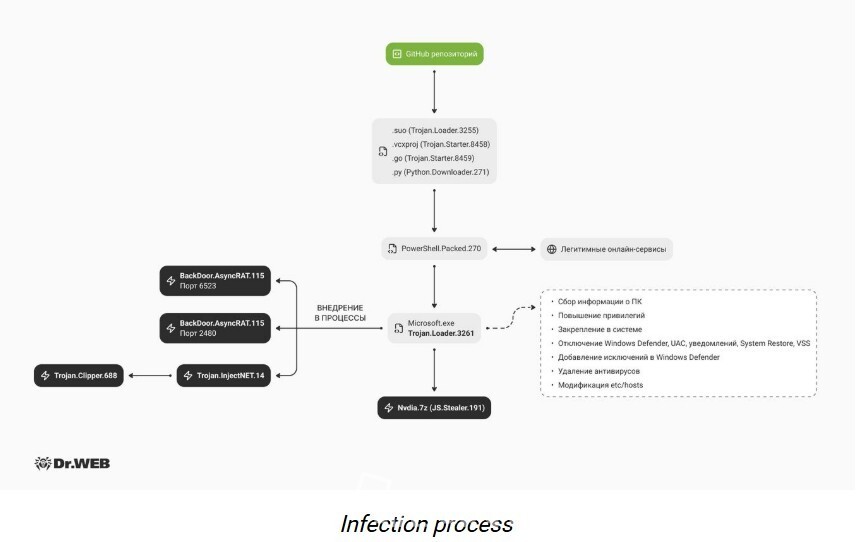
Attackers posted malicious projects disguised as security tools on GitHub, tricking security experts and developers into infecting Windows PCs. On November 5, Russian security company Dr.Web published a report analyzing the attack.
Key points
- The repository was disguised as a tool for organizing results from a fake network scanner.
- Malicious commands were hidden so that they would run first during the process of building the project.
- Once infected, the PC receives a program for remote control and malware that changes cryptocurrency wallet addresses.
- It also steals VPN and FTP login information and messenger authentication data and sends it to the attackers.
Why it matters
Security experts and developers often run external tools directly, so even projects in public repositories should be checked for safety before they are run.
Original source
깃허브에 가짜 보안도구 심어 해킹, 윈도 PC 2,000대 이상 감염
데일리시큐 · Nov 7, 15:13 KST
Read on 데일리시큐 ↗AI summarized the original article. Check the original for accuracy. Copyright belongs to 데일리시큐.
GitHub · Ranking and more news
More from this field
- Designers Say Ssense's Website Shows Their Clothes Inaccurately
Designer Reese Cooper noticed his RCOS puffer coat looked distorted on the luxury retailer Ssense's website, with a chest hook drawn far too large. Ssense said some site images came from a "virtual try-on" program, though it would not say whether that program uses AI.
The New York Times · Nov 21, 06:16 KST - Korean Firms Build Three-Way AI Push: Anthropic Stake, HBM Chips, Claude Rollout
Korean companies are expanding their roles in the global AI market around Anthropic's IPO. SK Telecom earned large paper gains from an early investment, while Samsung Electronics and SK hynix are strengthening chip supply ties. Samsung SDS and LG CNS are bringing Anthropic's Claude model into the business AI market.
뉴스웨이 · Nov 21, 06:10 KST - MIT and IBM Team Probes Gaps in Multimodal AI Understanding
MIT and IBM researchers are studying where today's multimodal AI models fall short, even when they handle text, images, and sound fluently. Their team, co-led by MIT's Jim Glass, builds new benchmarks and training methods that need less labeled data. This Q&A walks through how the project started and how it has evolved.
MIT News · Nov 21, 06:00 KST - Leaky AI Supply Chain Exposes Secret User Data at Alarming Rate
A research test sent nearly two million prompts with fake but working secrets through a network of AI services to see where they ended up. Many of the secrets were stolen, and attackers used them to reach cloud accounts. The results point to weak protection of customer data along the chain.
Ars Technica · Nov 21, 05:59 KST