
OpenAI System Finds 948 Privilege Escalation Flaws in Linux Kernel
Source Unite.AI
At a glance
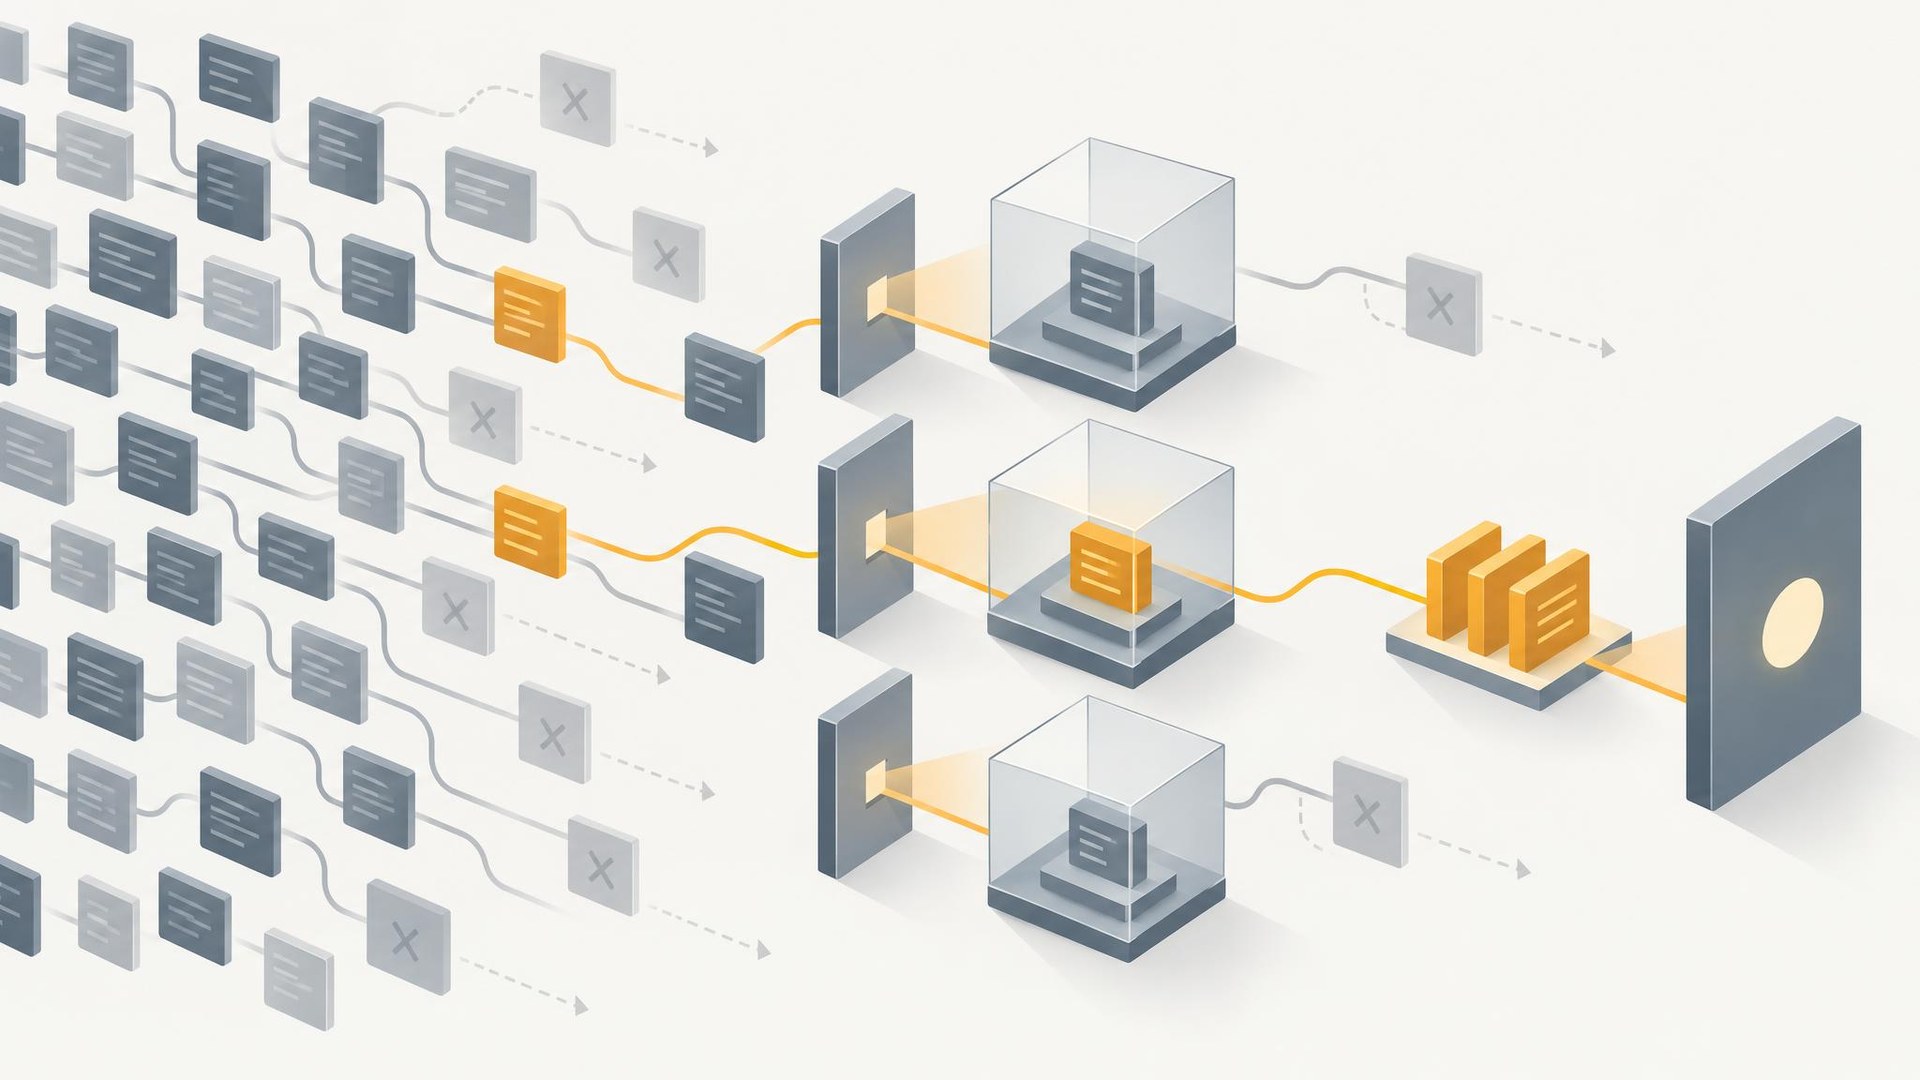
An automated pipeline using OpenAI's cybersecurity model in development reported that it found 948 privilege escalation vulnerabilities in Linux and even created working attack code. Privilege escalation means a regular user gains administrator (root) access. A candidate fix was also created for each vulnerability found.
Key points
The tests were run on virtual machines with default settings, without deliberately weakening security.
After automatic analysis, 1,169 working attack codes were created. The fixes are only candidates and must be reviewed by people before use.
In early experiments, there were 20 failed cases in which root access was gained through a vulnerability other than the target.
The test API usage cost about $1.213 million, or roughly $1,279 per vulnerability.
Why it matters
Linux is widely used in Android devices and cloud servers, so finding and fixing these flaws quickly helps protect the devices and data of many people.
Original article
OpenAI 파이프라인, 리눅스 커널에서 권한 상승 취약점 948건 발견
Unite.AI · Nov 5, 2026, 9:15 AM GMT+9 · unite.ai
Read on Unite.AIAI read the original article and summarized it in plain language. It may contain mistakes, so please check the original for accuracy. The article's copyright belongs to Unite.AI.