
Attackers Hijack GitHub Accounts to Scan 60,000+ Repositories, Steal Credentials from At Least 1,806
Source 데일리시큐
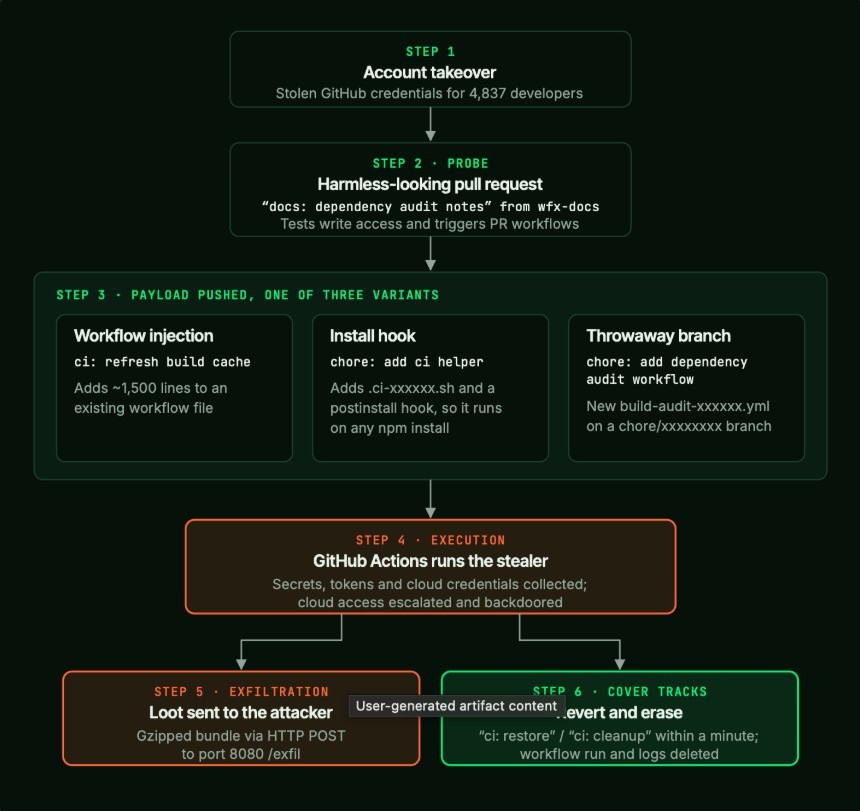
At a glance
Attackers used hijacked developer accounts to get into GitHub repositories and steal credentials used to build and deploy software. Security firm Endo Labs published a report on November 12. The attack, called wfx, was first seen on November 10, and how the first account was taken over is still unknown.
Key points
The attackers checked access rights across 61,764 repositories.
Traces of malicious code were found in 8,926 repositories.
Credentials were confirmed to have left at least 1,806 repositories.
The attackers planted malicious code in GitHub Actions, the automation tool that builds and tests code, to target cloud keys and package deployment tokens.
Why it matters
If a development team's keys and tokens are stolen, a company's cloud and deployment systems can be breached, so Korean development teams should check for signs of this attack.
Original article
탈취한 깃허브 계정으로 6만여 저장소 탐색…최소 1,806곳서 자격증명 탈취
데일리시큐 · Nov 13, 2026, 2:39 PM GMT+9 · dailysecu.com
Read on 데일리시큐AI read the original article and summarized it in plain language. It may contain mistakes, so please check the original for accuracy. The article's copyright belongs to 데일리시큐.