



AI · អត្ថបទ
Cursor Blames Exposed Access Key at Fireworks AI for Breach, Malicious Extension Pushed
Unite.AI ·
មើលត្រួសៗ
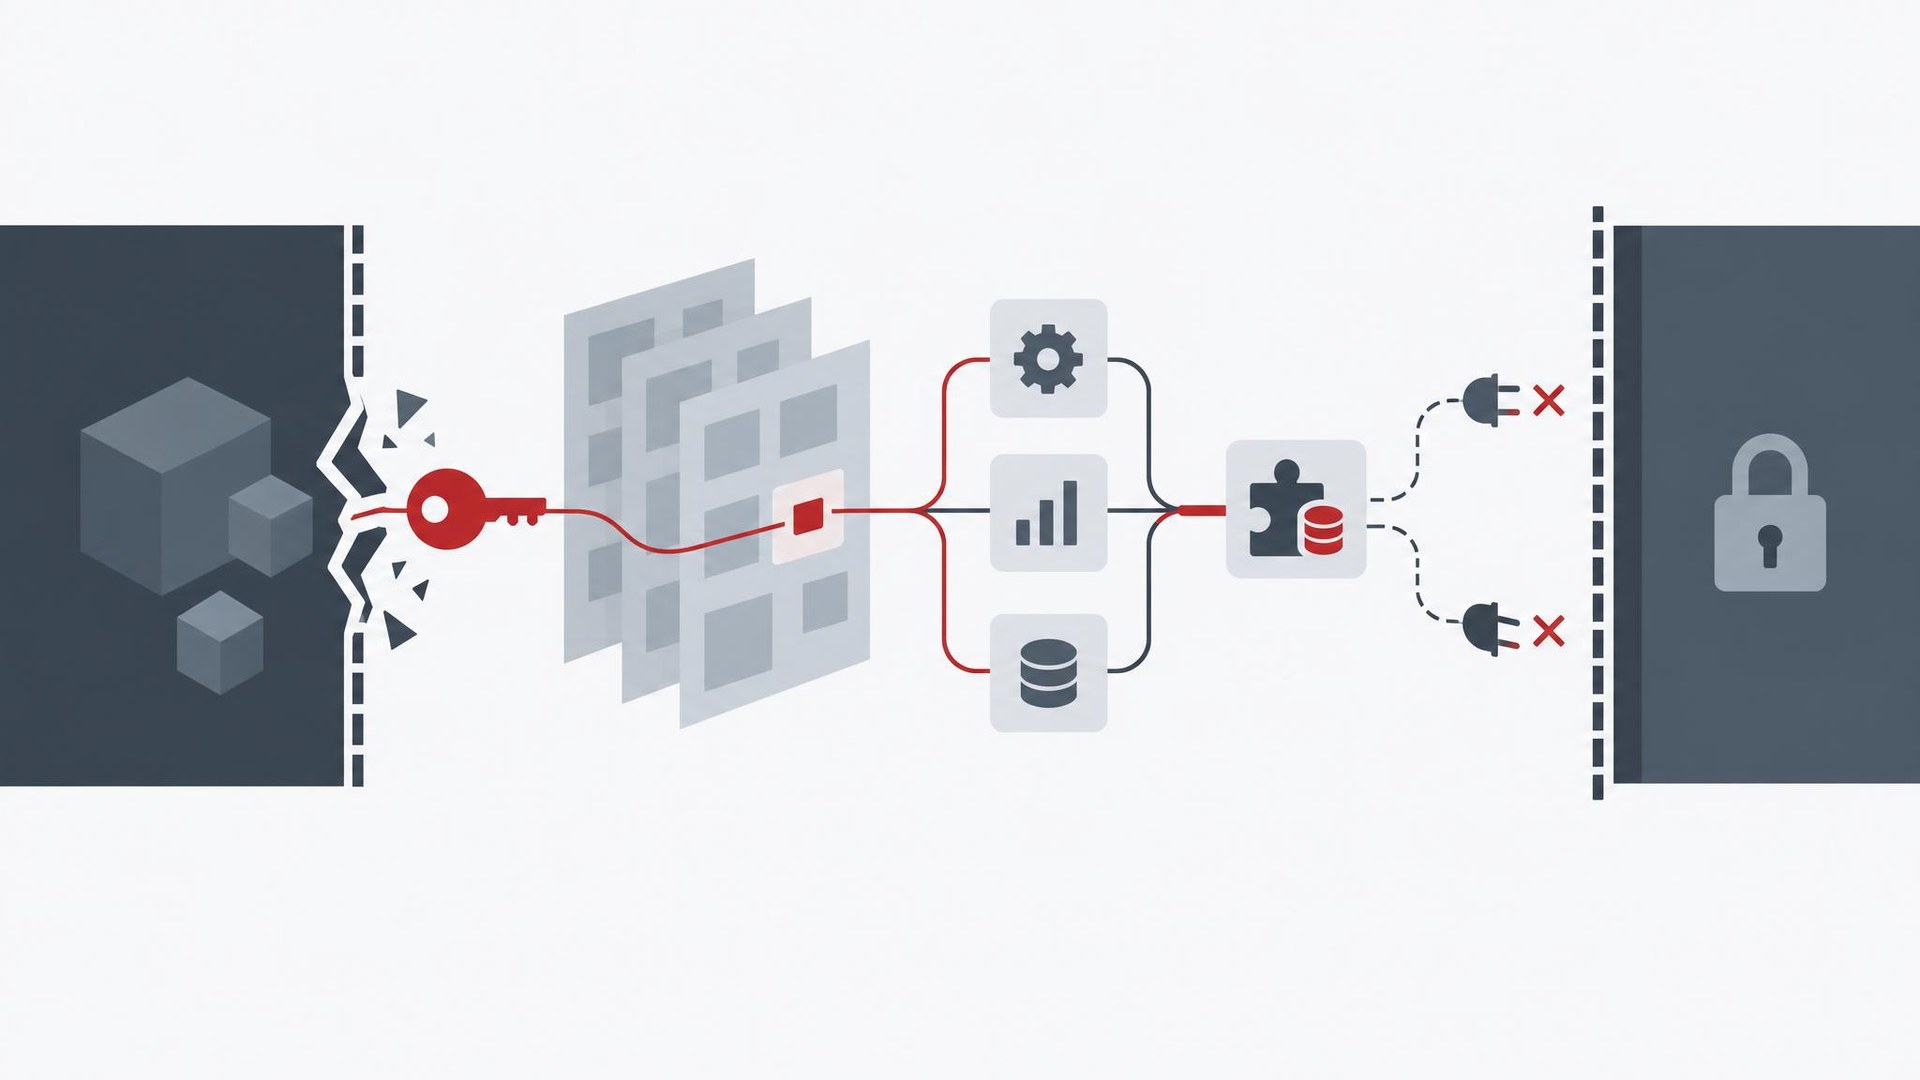
Cursor said attackers used an exposed access key from Fireworks AI to copy past coding-agent activity records and credentials. They then reached some of Cursor's software tools and pushed a malicious Claude Code extension build. Cursor says fewer than 0.01% of customers had API credentials exposed.
ចំណុចសំខាន់ៗ
- Attackers used a Cursor access key exposed through Fireworks AI to copy a read-only data bucket.
- The bucket held limited coding-agent activity records, mostly from 2025, from sessions without Privacy Mode.
- Some records contained credentials that let attackers reach some hosted software tools Cursor uses.
- Cursor says fewer than 0.05% of users without Privacy Mode had activity records exposed and that it notified them directly.
ហេតុអ្វីវាសំខាន់
Cursor is a widely used AI coding tool, and this breach exposed some user records and credentials. Users and admins may need to rotate keys and watch for the malicious extension.
ប្រភពដើម
Cursor, Fireworks AI에서 노출된 액세스 키가 침해 원인이라고 밝혀
Unite.AI · Nov 14, 10:34 KST
Read on Unite.AI ↗AI summarized the original article. Check the original for accuracy. Copyright belongs to Unite.AI.
ការផ្សាយផ្សេងទៀត
Cursor · ចំណាត់ថ្នាក់ និងព័ត៌មានបន្ថែម
បន្ថែមពីវិស័យនេះ
- OpenAI Shows How to Claim a Shopify Store in ChatGPT
This video shows how to claim your business in ChatGPT by connecting your Shopify store. You can start in Business Hub or the Shopify App Store. After connecting, you can manage your business information to control how your store appears in ChatGPT.
OpenAI 공식 YouTube · Nov 21, 05:48 KST - OpenAI Sharply Cuts Success of Attacks on GPT-6.2 Astra and Sol Reasoning
OpenAI has greatly strengthened its defenses against attempts to pull the hidden reasoning out of its latest models, GPT-6.2 Astra and GPT-6.2 Sol. In its own internal tests, the success rate of these attacks fell sharply, and OpenAI says it is now bringing some of these improvements to GPT-6 Astra too.
The Decoder · Nov 21, 05:31 KST - Amazon Textract Insights Launches for Verifiable Document Data Extraction
Amazon has launched Amazon Textract Insights, a generative AI feature that pulls specific fields from documents. Users describe the data they want in plain language and get results with a confidence score and the page each value came from. Mixed files, such as a mortgage packet, can be split and matched automatically.
Amazon AWS Machine Learning blog · Nov 21, 05:22 KST - Etsy Sellers Close Shops Over New Policy Allowing AI Training on Their Work
Many longtime sellers on Etsy, the handmade goods marketplace, have closed their shops over new terms that let the company and its partners use seller content to train artificial intelligence. The terms take effect on Dec. 16. Etsy has defended the policy.
The New York Times · Nov 21, 05:19 KST